The Integral Management Society · GenevaTEGRITY.AI / HOME / 2026-09 · v10.2
Operational Integrity
Tegrity.AI is an applied research, engineering and pre-standardization group of The Integral Management Society, a Swiss non-profit association based in Geneva. It advances AI Integrity Management through research, architecture, the review and development of standards, and technology for the common good.
Contents
§ 01
Ecosystem Awareness
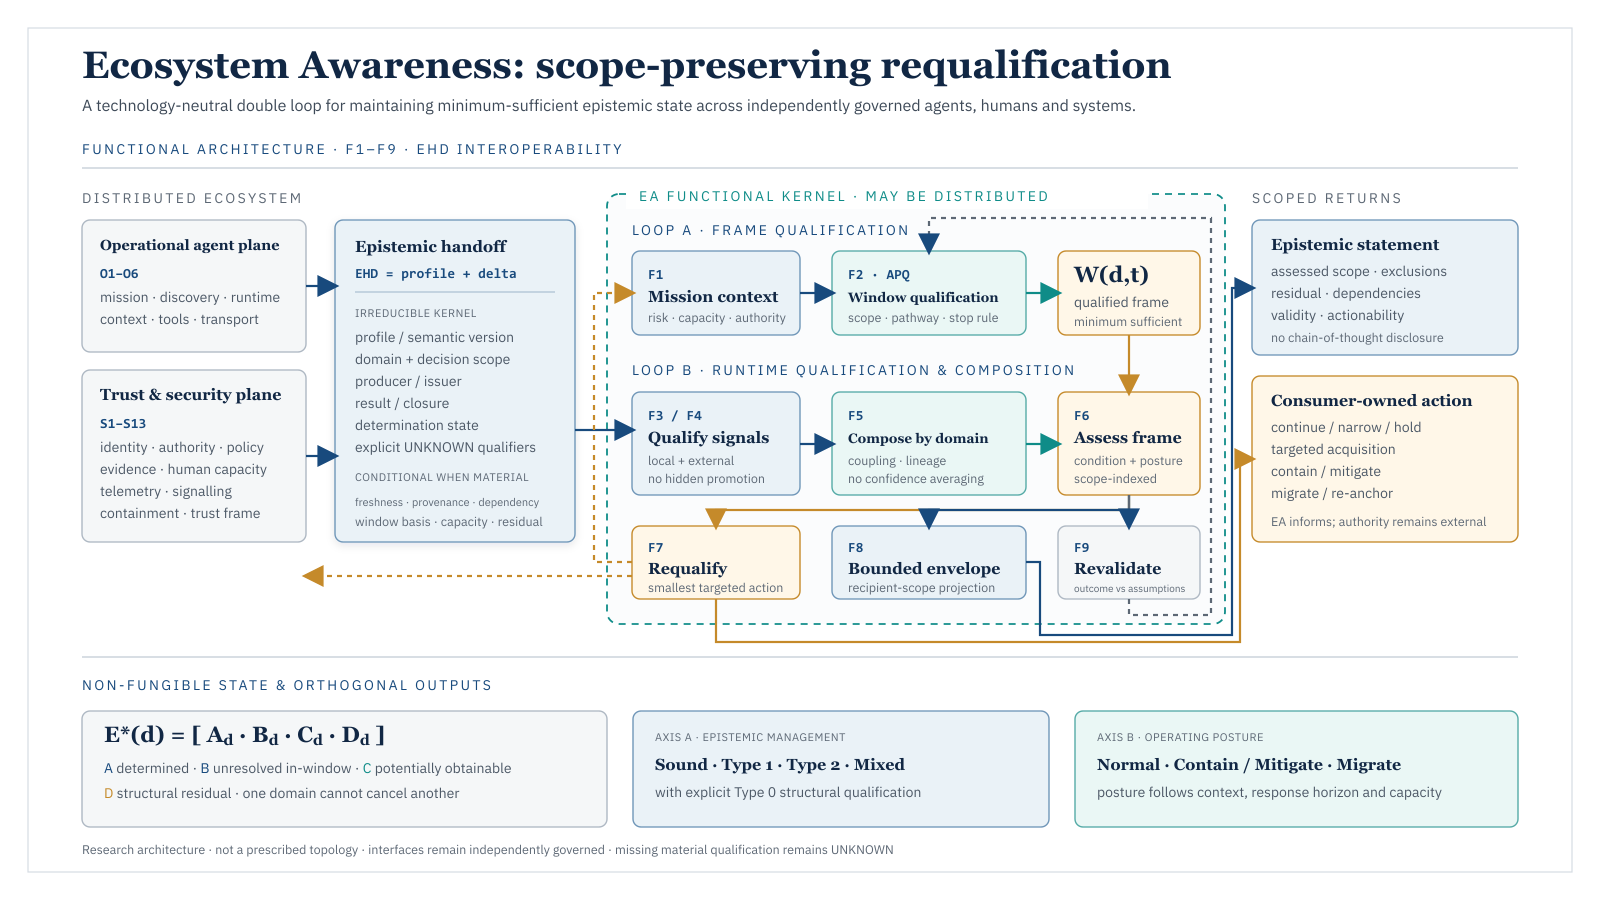
In agentic systems, locally justified decisions can coexist with global indeterminacy. Ecosystem Awareness maintains a justified epistemic posture by continuously relating residual uncertainty to mission risk, determination capacity and the value of knowing more.
It preserves and communicates that posture across agent, human and system boundaries, whether the ecosystem is centrally orchestrated or not. For example, human oversight is itself a determination-capacity constraint: the relevant human may be known and authorised, yet unavailable within the useful decision window.
Ecosystem Awareness is a candidate pre-standardization architecture being developed publicly through ITU-T FG-TIDA contributor work to make system-level epistemic state legible and interoperable across independently governed human and agentic components.
Its differential is not uncertainty quantification, observability, human oversight or orchestration by themselves. It combines:
- Scoped epistemic state — what is determined, unresolved, potentially knowable and structurally residual.
- Non-fungible composition — confidence in one domain cannot erase uncertainty in another.
- Risk/capacity requalification — expand, narrow or stop determination according to mission risk, capacity and response horizon.
- Transport-neutral handoff — preserve the minimum scope, uncertainty, residual and dependency semantics needed across boundaries without a common internal reasoning model or central orchestrator.
Some distinctive features:
- Reduces false systemic confidence by preventing local closure, duplicated evidence or confidence in one domain from being laundered into global certainty.
- Improves the risk/resource frontier by directing observation, search, escalation and human attention only where additional determination has material decision value — and stopping when it does not.
- Enables heterogeneous agents, vendors and independently governed systems to interoperate epistemically without requiring a shared uncertainty model, central controller or disclosure of internal reasoning.
- Supports targeted requalification: when assumptions fail, the system can revisit the affected scope rather than rerunning or over-controlling the entire workflow.
Selected reading: EA foundations · general interfaces · Theme #13 (contributor @dakleyer) · EA contribution (contributor @dakleyer) · Theme #16 (contributor @dakleyer)
EA / canonical corpusExplore the corpus index7 sections · 50 entries
Open the canonical GitHub README · Same reading order and document links.
| 00Problem-to-architecture reading route | |
|---|---|
| R1 | Foundation and principlesRead the integrated theory and control matrix before treating an architectural proposal as a requirement.02 · principles and control matrix |
| R2 | Canonical requirementsS1–S14, T1–T4, H1–H6 and the KPI/falsification protocol in the single current requirements document. |
| R3 | 100 Million Tokens · reference failure scenarioA concrete multi-system case tracing information loss, requirements and deterministic quality-gate dispositions. |
| R3a | Microsoft Agent 365 implementation profileProduct-specific stress profile for documented registry, identity, security, compliance and observability capabilities. |
| R3b | LangGraph / LangSmith implementation profileOrchestration-runtime stress profile for durable execution, observability, evaluation and latent regime change. |
| R4 | Smart-city mobility divergence · reference scenarioTechnology-neutral multi-actor mobility case with noisy, stale and partly dependent telemetry. |
| R4a | FIWARE NGSI-LD / Orion-LD implementation profileContext-broker stress profile comparing standard, strong federated and post-pivot implementations. |
| R4b | AWS IoT TwinMaker / IoT Core implementation profileDigital-twin and event-system stress profile with hidden dependency, timestamp and model-validity pivots. |
| R5 | Canonical architecture topologyShared reading key for Ω, U, R_U, W(d,t), positions A–D, failure types and F1–F9 handoffs. |
| R6 | Canonical architecture benchmark and evidence v0.2The sole current benchmark route: EA-H1–EA-H4, B0–B3 fair comparison, falsifiers and evidence grades. |
| 01Current architectural argument — read 01 to 06 | |
| 01 | Integrated Foundational Theory v0.5Residual indeterminacy, ecosystem change, neighbouring architectures and the shared concept dictionary.v0.4 source 12345 |
| 02 | Epistemic Safety Principles & Control Matrix v0.4Four epistemic poles, non-fungible composition and twelve controls for internal and received signals.part 2part 3 |
| 03 | Functional Architecture v0.4Qualification loops, result axes, F1–F9 functions, control postures and component handoffs.part 2part 3 |
| 04 | General Functional Interfaces & Agentic Security v0.4Transport-neutral contracts, general interfaces and agentic-security boundaries without a supercontroller.part 2part 3 |
| 05 | Provisional Cross-Theme Contracts v0.4FG-TIDA theme mappings as one implementation example of the general interface architecture.part 2part 3 |
| 06 | Canonical Architecture Benchmark & Evidence v0.2EA-H1–EA-H4, B0–B3 fair comparison, decisive falsifiers, evidence grades and 00E/00F corroboration.v0.4 source 123 |
| 02Foundational source and extension annexes | |
| 01A | Two Foundational OriginsDerivation of the two origins: epistemic residual and changing ecosystem. |
| 01B | EA ↔ MSCACandidate EA–MSCA inputs, outputs, scope, authority and requalification boundaries. |
| 01C | EA ↔ Regime Awareness / EWSGood-Enough detector properties and candidate EA–Regime Awareness payloads and tests. |
| 01D | Joint EA / MSCA / RA operationSame-operation binding, permit precedence, UNKNOWN handling, cost and race conditions. |
| 01E | EA ↔ extensible DAOS model caseDAOS facts, challenges and extensibility mapped to bounded EA functions and use-case profiles. |
| 03Validation profiles — one case, four diagnostic lenses | |
| V0 | DAOS→EA engineering masterclassWorked mobility case, challenge mapping, test seams and fair comparison protocol. |
| VF | Frozen validation familyThe frozen family connecting one source case to four distinct validation lenses. |
| UC-01 | Action-time frame requalificationChanged context, stale commitments, response time and proportionate frame requalification.prior source parts |
| UC-02 | Bounded evidence determinationIncomplete or dependent evidence, structural residual and acquisition burden. |
| UC-03 | Effective human oversightAvailable authority and human capacity; approval does not repair conflicting evidence. |
| UC-04 | Scope-indexed compositionLocal validity versus whole-system support across independently governed domains. |
| ITP | EA-ITP-01 · interoperability testSeparate interoperability profile for EHD and Theme #13; not a fifth EA use case. |
| VR | Validation reading noteHow to read validation sources, freezes and aliases without confusing their status. |
| M | Canonical corpus manifestFile and verification status for the current canonical corpus. |
| 04Research lineage | |
| I | Naturalistic foundations & agentic lifecycle inversionProtected system versus changing ecosystem, agentic lifecycle inversion and minimum sufficiency. |
| II | Minimum control & multi-optimaObjective Envelope, feasible sufficient regions and plural local or Pareto alternatives. |
| III | Semantic Window & Good-Enough Early WarningAction-relative observation window, useful warning, failure cases and response trade-offs. |
| IV | Signalling without required cooperationConditional signals between independent actors, correlation limits, privacy and no global command.part 2 |
| V | FG-TIDA reference-model proposalProposed objective-to-control-to-warning-to-signalling reference questions for FG-TIDA.part 2part 3 |
| P | Architectural PrinciplesPrinciples behind bounded qualification, composition and architectural responsibilities. |
| 3D | Three Dimensions of IndeterminacyThree different forms of indeterminacy and their technical consequences.234 |
| D | Deep Derivation MapConceptual derivation from source arguments to current architecture. |
| C | Prompt-to-Canon Conservation MatrixTrace of earlier prompts and source ideas into the current canon.23 |
| APQ | APQ Corpus Change RecordControlled record of corpus changes and conservation checks.2 |
| 05Governance and provenance | |
| F0 | Initial freezeOriginal frozen source snapshot for provenance. |
| F1 | Maintenance freeze manifestMaintenance freeze status and controlled source changes. |
| FR | Maintenance reading noteReading guidance for the maintenance freeze and its boundaries. |
| FP | FG-TIDA public footprintPublic FG-TIDA discussion footprint without claiming adoption. |
| PR | Public provenancePublic source and contribution provenance. |
| M | Canonical corpus manifestFile and verification status for the current canonical corpus.earlier manifest |
| H | Historical public sourcesEarlier public versions retained as sources, not current chapters.benchmark v0.4benchmark v0.5 aliasUC-01 earlier alias |
| 06Independent linked corpora | |
| DAOS | Delegated Authority OS case packageSeparate FG-TIDA DAOS case corpus: source case, extensions, challenges and mappings. |
| MSCA | Minimum Sufficient ControlSeparate MSCA corpus: objective-bound sufficiency, submitted input and working interfaces.FG-AI4SSC inputworking paper |
| EWS | Minimalistic Regime-Aware Early Warning SystemsSeparate EWS corpus: detection sufficiency and bounded response safety. |
§ 02
Minimum Sufficient Control Architecture
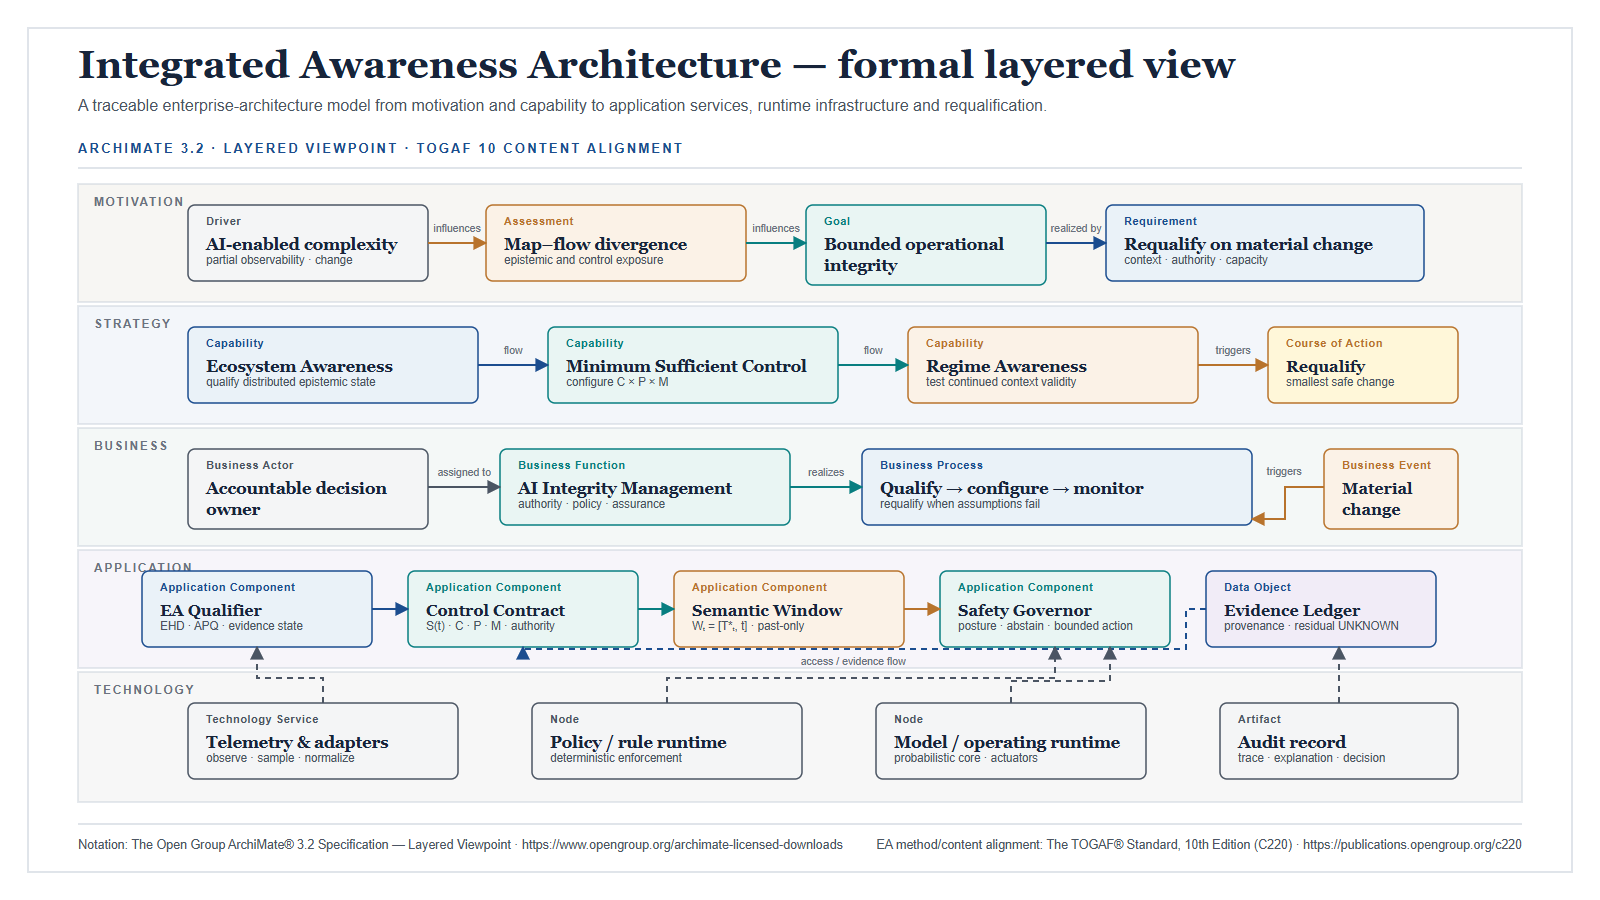
As an operational output of Ecosystem Awareness, Minimum Sufficient Control Architecture (MSCA) defines the least intervention-intensive configuration that can keep a system within its declared Objective Envelope under the current ecosystem, operating-context and regime conditions.
The Objective Envelope S(t) constrains a joint search over coordination scope (C), operational mechanisms (P) and enabling means (M). Sufficient configurations are then compared by justified burden.
It is not a single global optimum or a fixed minimal stack. Multiple control architectures may be sufficient under the same Objective Envelope, with different allocations of observation, early warning, containment, migration, ecosystem signalling, redundancy, human oversight and feedback. The relevant architecture is the one that remains within the feasible sufficiency region with the lowest justified burden for the current context.
Advantages:
- Resource-proportional control — allocates observation, control and human capacity where they materially support the Objective Envelope, reducing coordination overhead and improving both local and system-wide efficiency.
- Architectural interoperability and mapping — expresses different architectures, resources, objectives and apparently different use cases through a common sufficiency model, enabling comparison and extension without imposing a single stack.
Ecosystem Awareness provides the requalification signal: when ecosystem or regime conditions change, the current MSCA may remain sufficient, require targeted adjustment, or require a different control posture.
FIELD → MODEL → IMPLEMENTATION
From field systems to implementable architecture
Tegrity.AI’s engineering lineage brings decades of implementation practice to this work. Requirements, code, operating records and failure conditions are examined before the transferable control problem is distilled into a bounded model. The documented xSeil mobility system is one field origin; MSCA interprets it retrospectively, not as a historical implementation of today’s proposal.
For enterprise rationalisation and resource reduction, MSCA starts with the objective and hard constraints, then compares candidate AI-enabled architectures by coordination scope, interventions and enabling means (C/P/M). The appropriate AI architecture is objective-specific, not a prescribed stack; a lighter configuration is preferable only if it still satisfies the Objective Envelope and preserves a viable response to changed conditions. The aim is to develop clear, lightweight guidelines from case tests so the model is easier to implement, while also informing standards-facing requirements—not claiming adopted standards or validated deployment.
Field evidence → bounded model → testable guidance Worked case and method
Current work: with industry, mapping agentic and pre-agentic systems against MSCA to reconstruct how objectives, context, controls and architectural choices evolve over time, and to test the same control logic across different domains and use cases.
ITU-T FG-AI4SSC (Focus Group on AI for Smart Sustainable Cities and Communities) covers system-level integration of AI-enabled urban technologies — requirements, interfaces, coordination, interoperability and assessment. This is where Minimum Sufficient Control was first submitted as a Focus Group input: read the submitted contribution, FGAI4SSC-I-097 (PDF).
Selected reading: MSCA working paper · minimum-control corpus · extensible mobility case · EA–MSCA interface
Two independent reading paths. Their source corpora remain separate from EA; the interface annexes above explain how they may connect.
MSCA / corpusMinimum Sufficient Control — reading index5 readings + neighbouring corpora
Canonical GitHub README · Same reading order; the submission remains in its own route.
- 01Architectural and standards working contextOriginal working note: Objective Envelope, coordination, mechanisms, means, research questions and claim boundaries.
- 02FG-AI4SSC input FGAI4SSC-I-097Submitted contribution and custody route. A focus-group input is not an adopted standard.
- 03MSCA working paperCurrent architecture, component handoffs and staged assessment; do not attribute later analysis to the submitted input.
- 04EA research lineage II — multi-optimaPredecessor account of feasible sufficient configurations, local and Pareto alternatives, and response capacity.
- 05EA ↔ MSCA interface annex 01B · Joint operation annex 01DCandidate EA–MSCA inputs and outputs; the linked 01D profile tests their same-operation composition with Regime Awareness.
Case and neighbouring corpora
Status: research and a posted focus-group input; no adopted ITU position, universal minimum or completed comparative validation.
DAOS / model caseDelegated Authority OS — case package6 canonical documents
Canonical GitHub README · Public pre-freeze working package for FG-TIDA discussion.
- 01Case design and pre-freeze working structureWhy this case is proposed, ideal pre-freeze design conditions and freeze logic.
- 02Annex I — Minimal Operational CaseThe concrete mobility case, public explanation, technical completion and next-use paths.
- 03Annex II — Case ExtensibilityUpward, downward and horizontal extension without changing core case semantics.
- 04Annex III — Challenges Exposed by the CaseS1–S14 solution challenges kept separate from the case facts.
- 05Annex IV — FG-TIDA ToR Mapping and TraceabilityCase and challenge links to the Focus Group Terms of Reference, with traceability limits.
- 06Annex V — Adjacent Standards and Research RelevanceControlled interfaces to neighbouring groups, standards and research; no adoption claim.
Status: public working material; no FG-TIDA or ITU adoption, endorsement or completed validation.
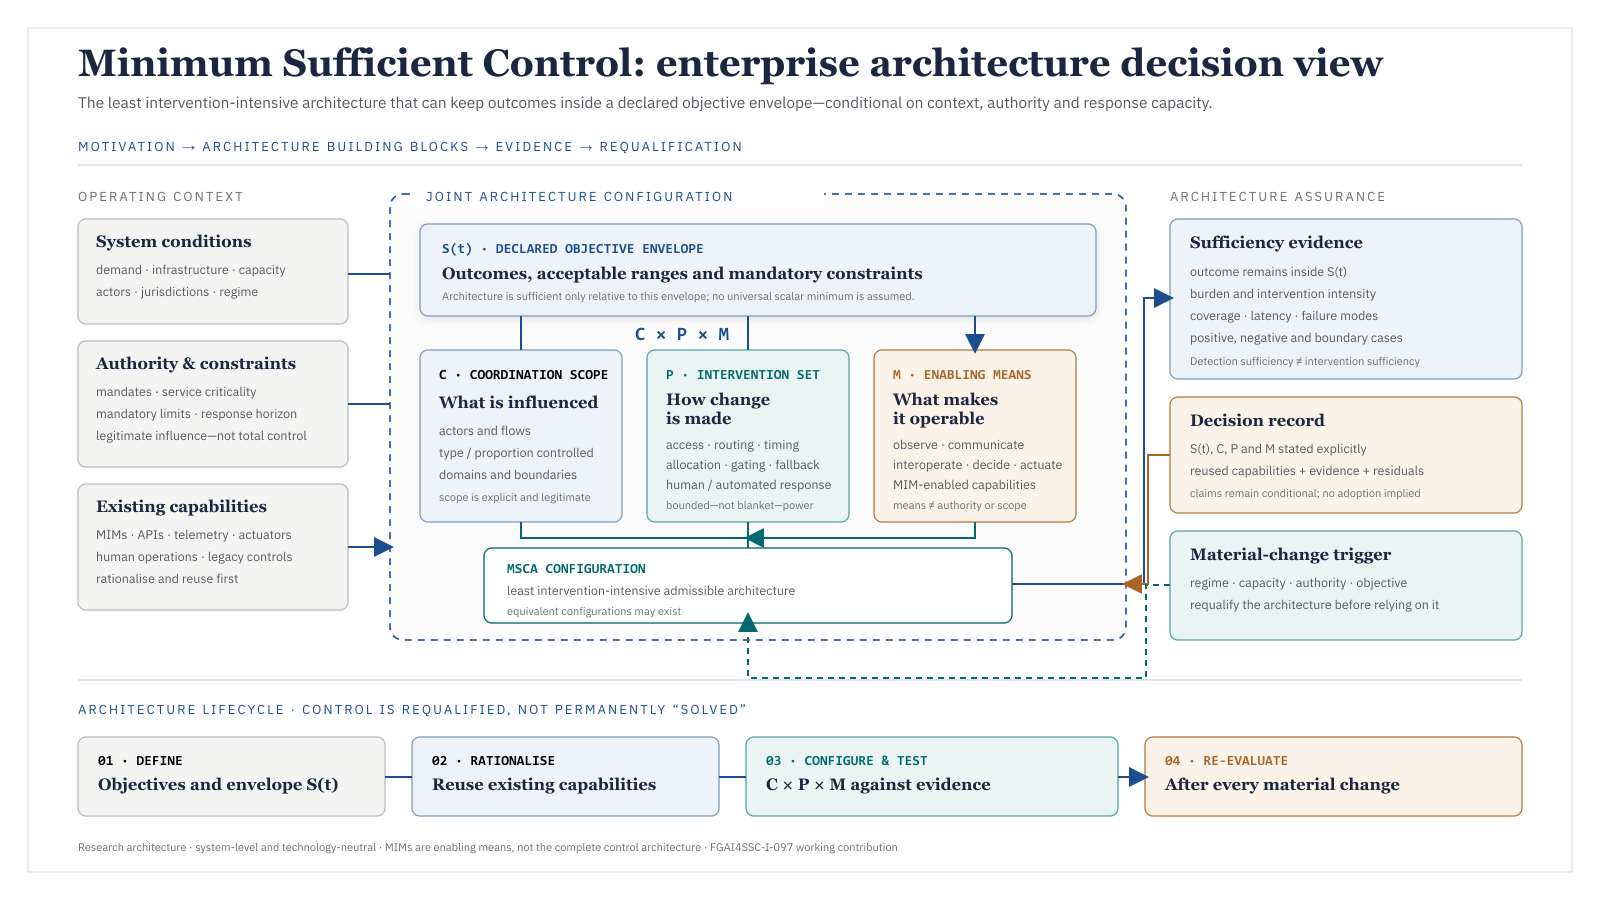 MSCA-01Objective-envelope qualification architecture
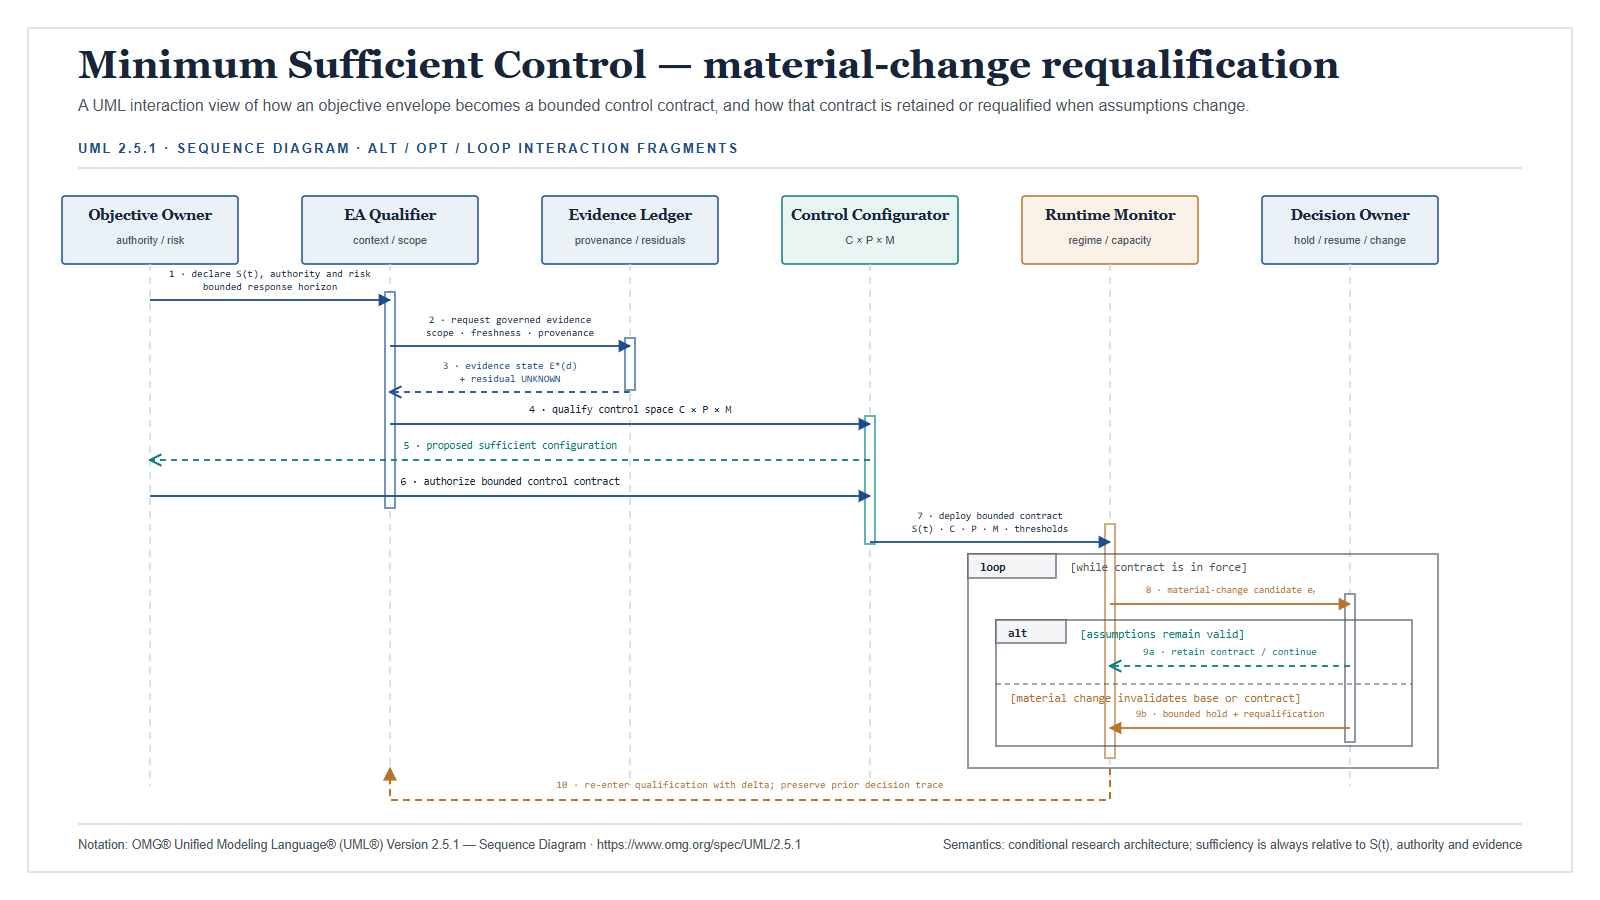 MSCA-02Material-change requalification sequence
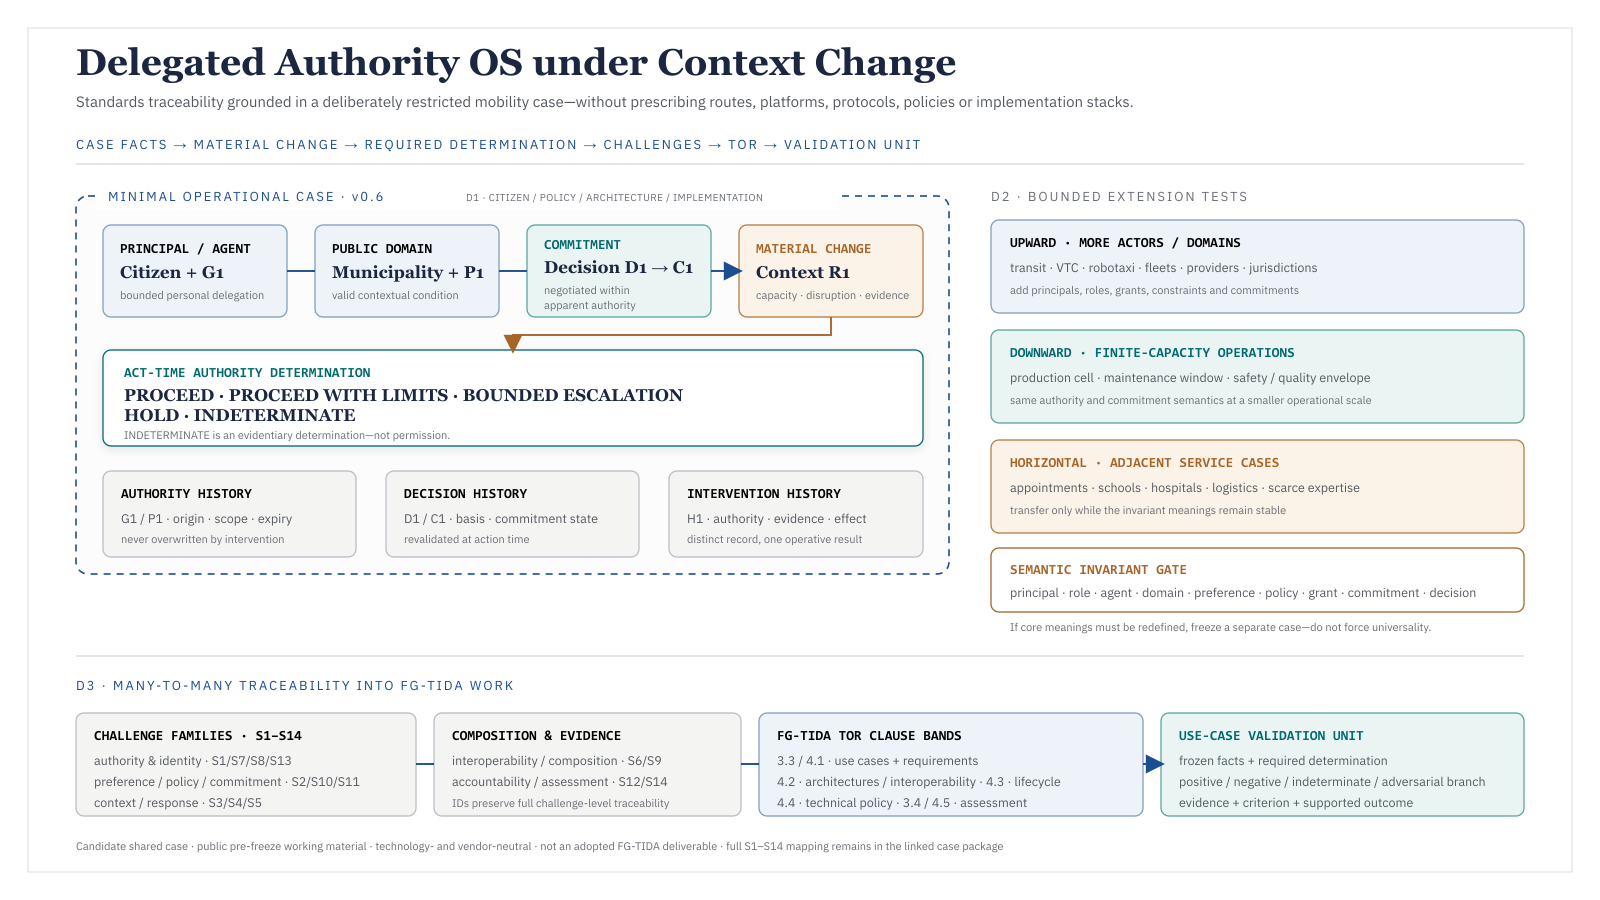 MSCA-03Case-to-validation standards traceability
§ 03
Regime Awareness / Sufficiently Good Early Warning
Regime Awareness is an important component of Operational Integrity. It links Ecosystem Awareness and MSCA by detecting when the operating conditions that justify observation, assessment and control are losing validity — even when the next regime is not known in advance. It is not forecasting: it asks whether present observable behaviour remains sufficiently compatible with the regime under which the current epistemic posture and MSCA are justified.
Because a real system cannot depend on a perfect detector, the pre-standardization object is a Sufficiently Good detector: a model- and domain-agnostic evaluation surface for whether detection is early, reliable and resource-proportionate enough to preserve useful action under the declared Objective Envelope and available response capability. Sufficiency is always evaluated relative to context; no preferred forecasting model, detector family or time-series method is imposed.
Concrete industrial detectors and operational solutions can therefore be compared against the same sufficiency benchmark across different systems, domains and series, rather than against an imaginary perfect detector.
Current work: research review with Universitat de València — QAVA (GIUV2026-019), covering concrete regime-awareness cases and the early-warning / Sufficiently Good detector architecture as part of the programme’s validation and pre-standardization work.
Selected reading: field cases · Good Enough EWS · H1–H3 validation proposal · EA–RA interface
See the full initiative index, with links to the underlying Field Notes series, in Research Initiatives.
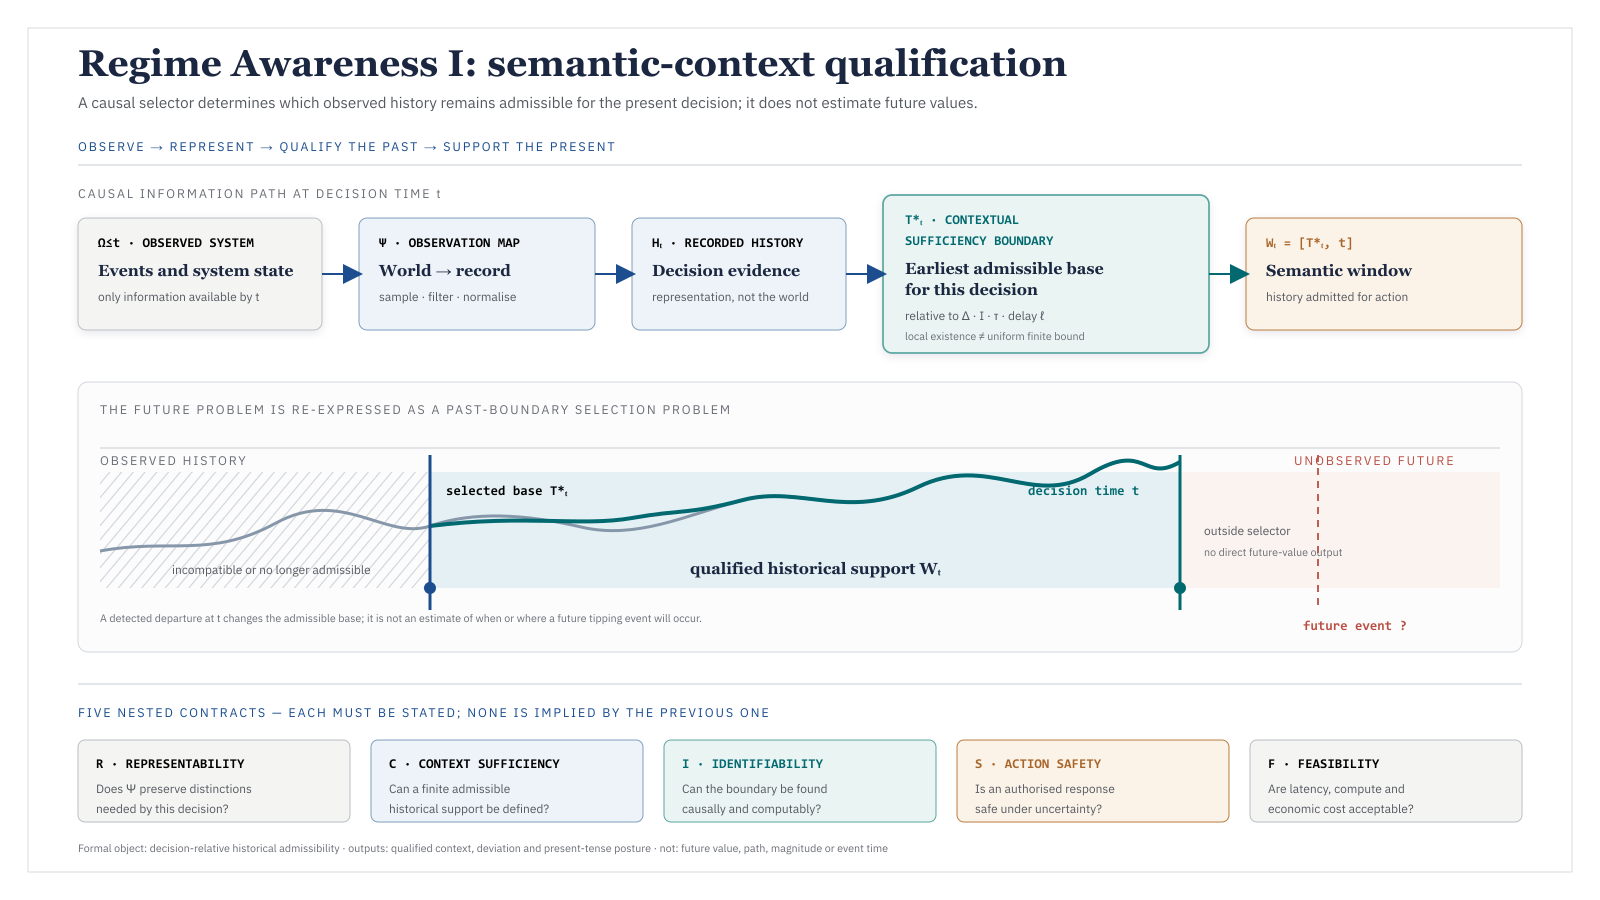 RA-01Semantic-window context architecture
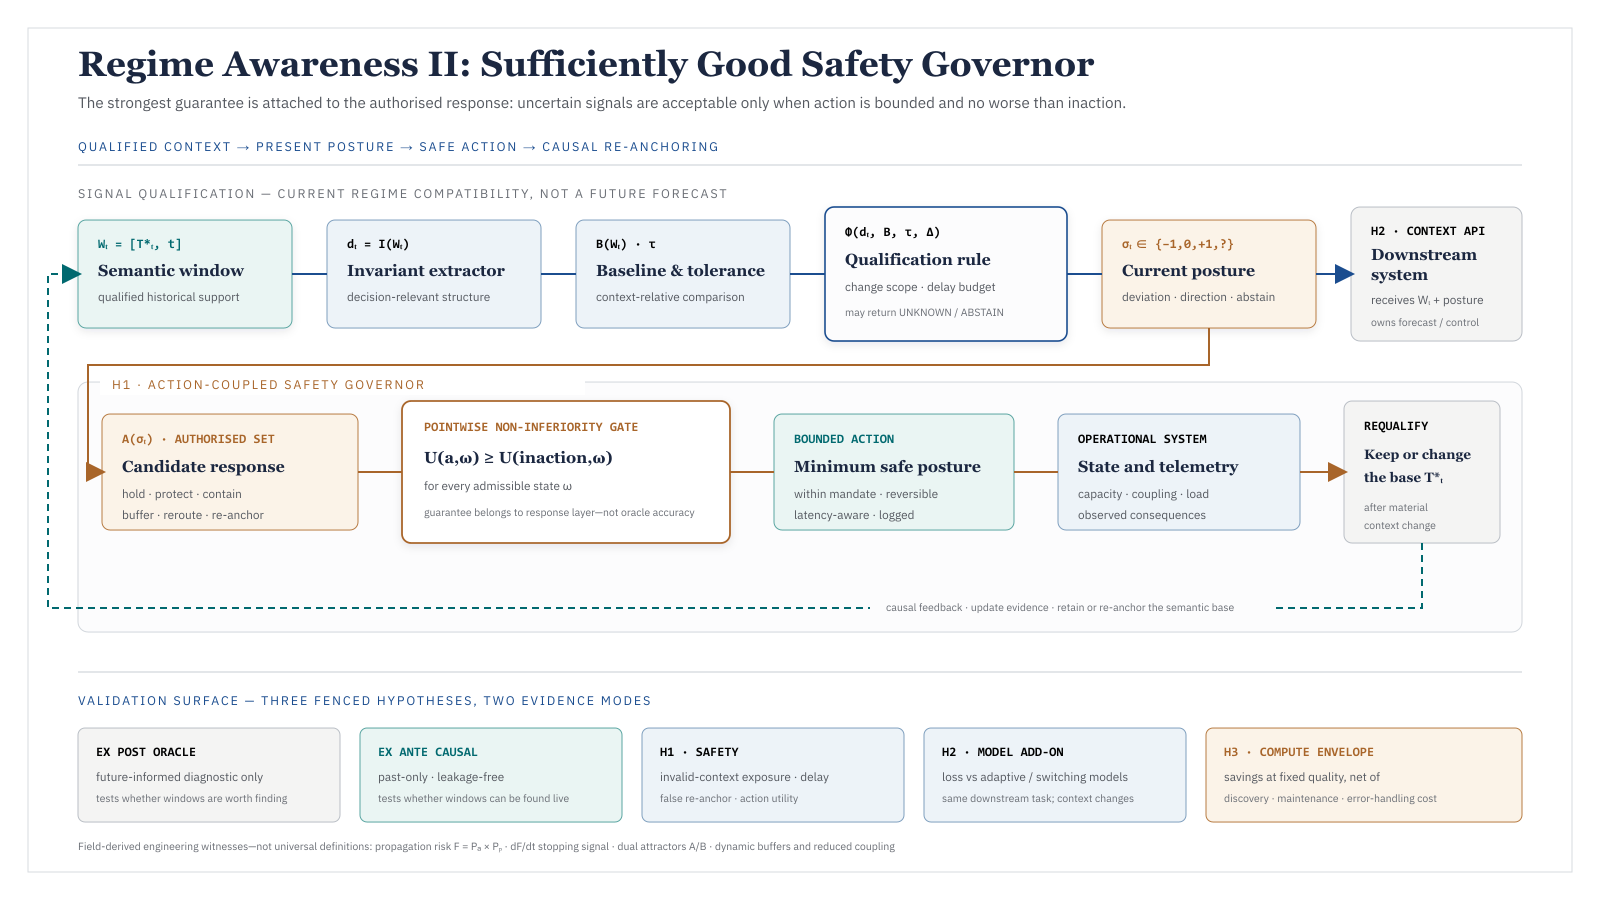 RA-02Warning-sufficiency validation surface
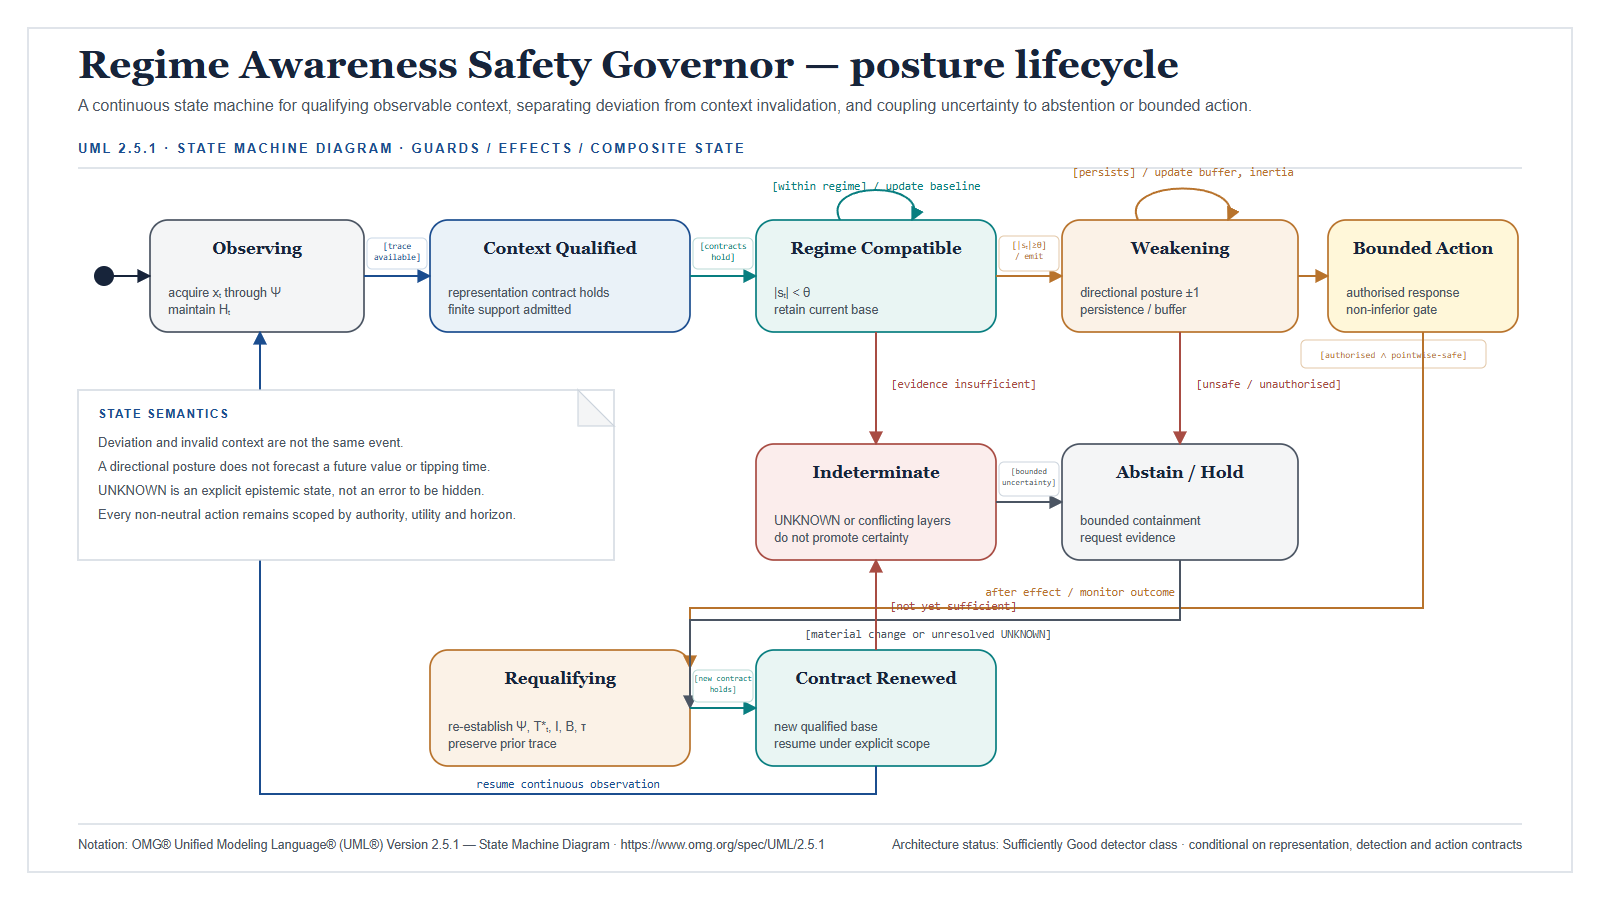 RA-03Safety-governor posture lifecycle
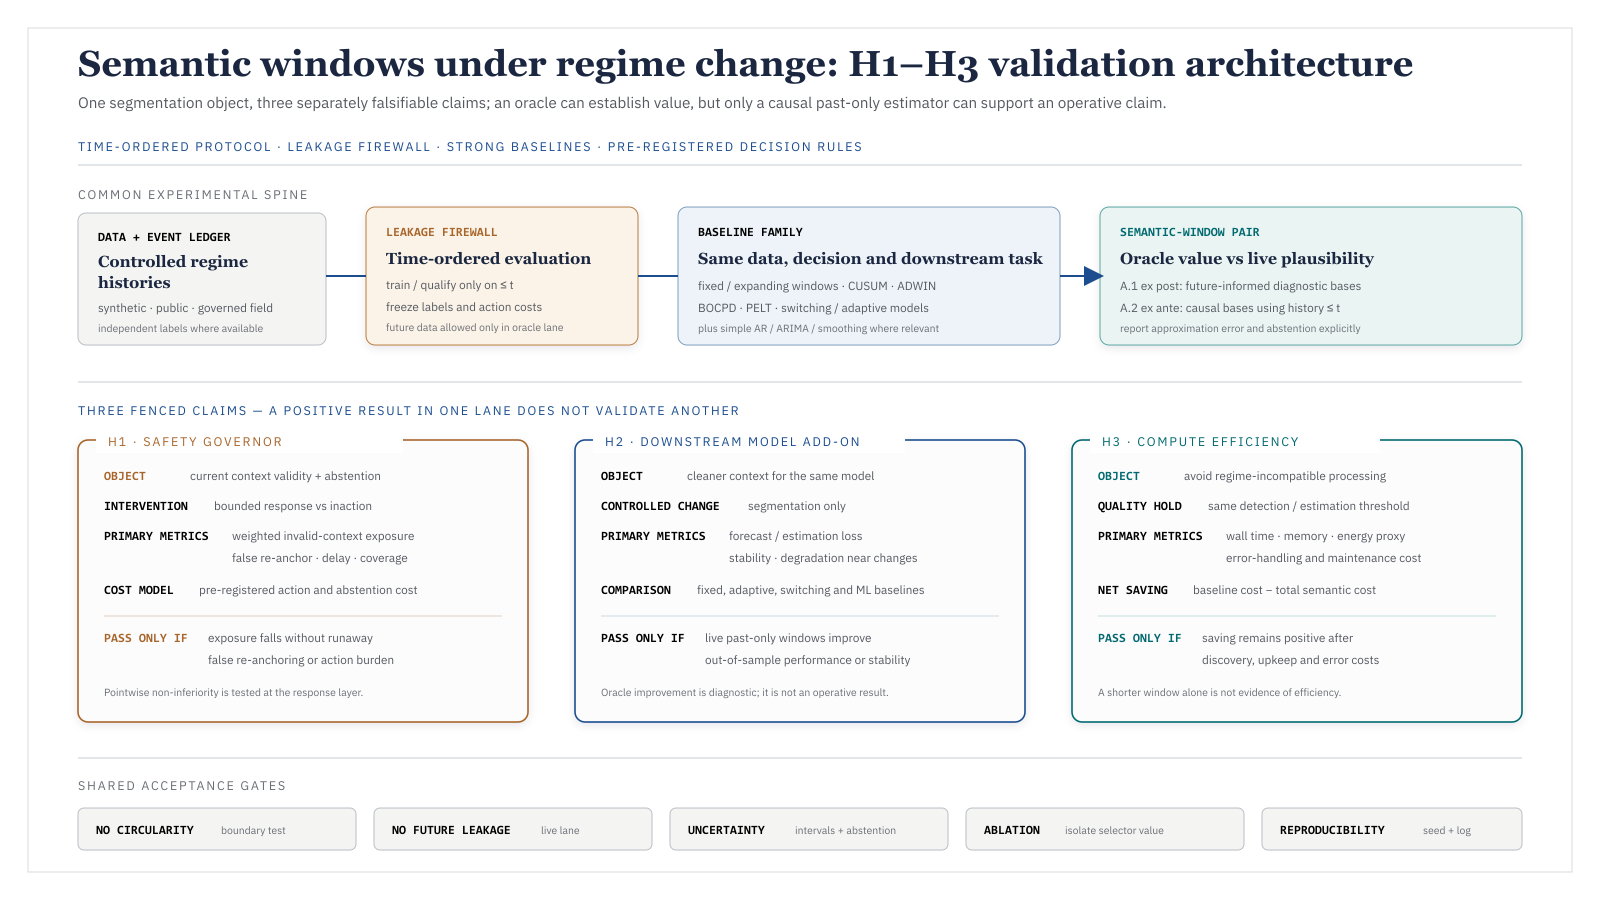 RA-04H1–H3 experimental architecture
 RA-05Causal selection and re-anchoring
Explanatory notebook
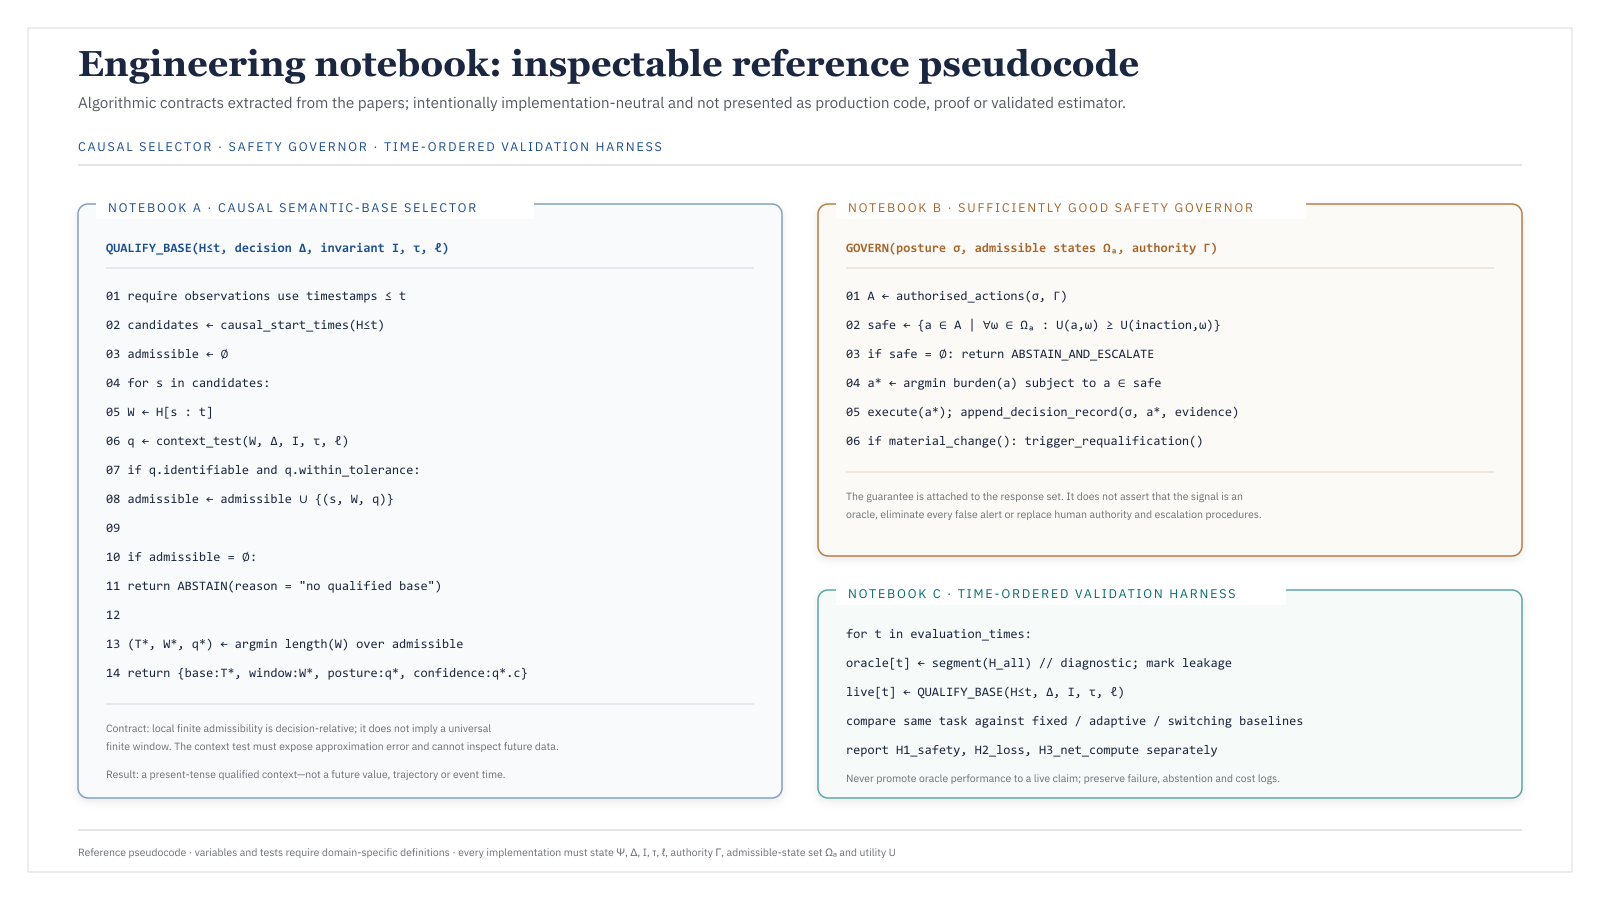
Selected executable examples behind the diagrams
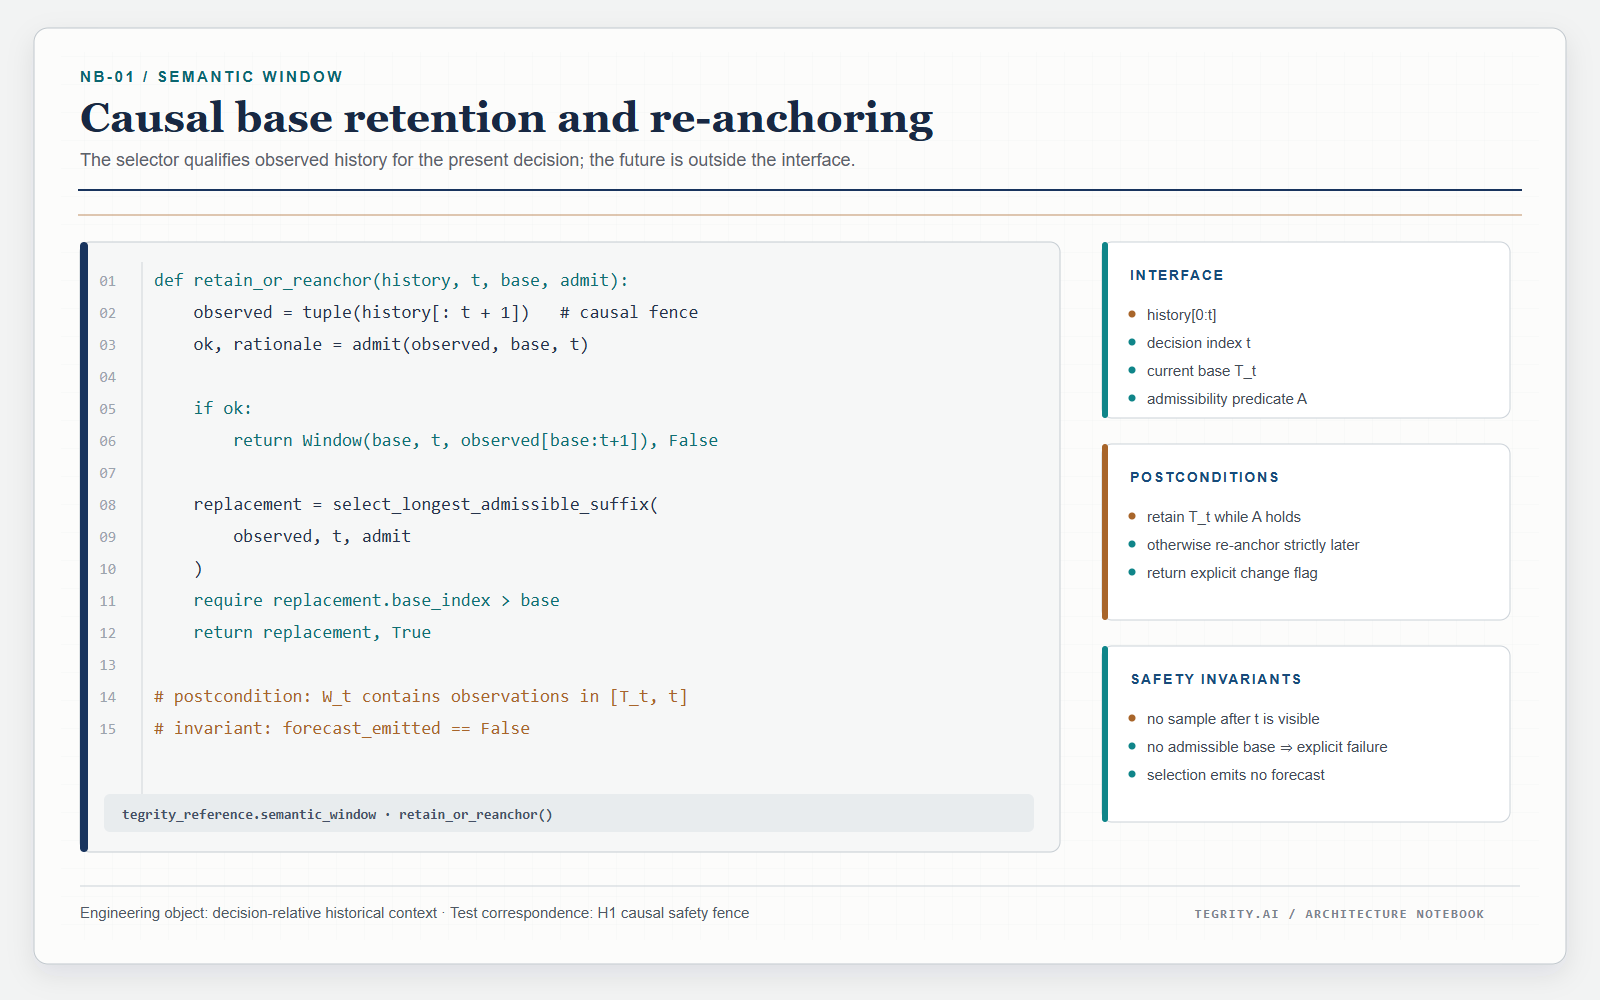
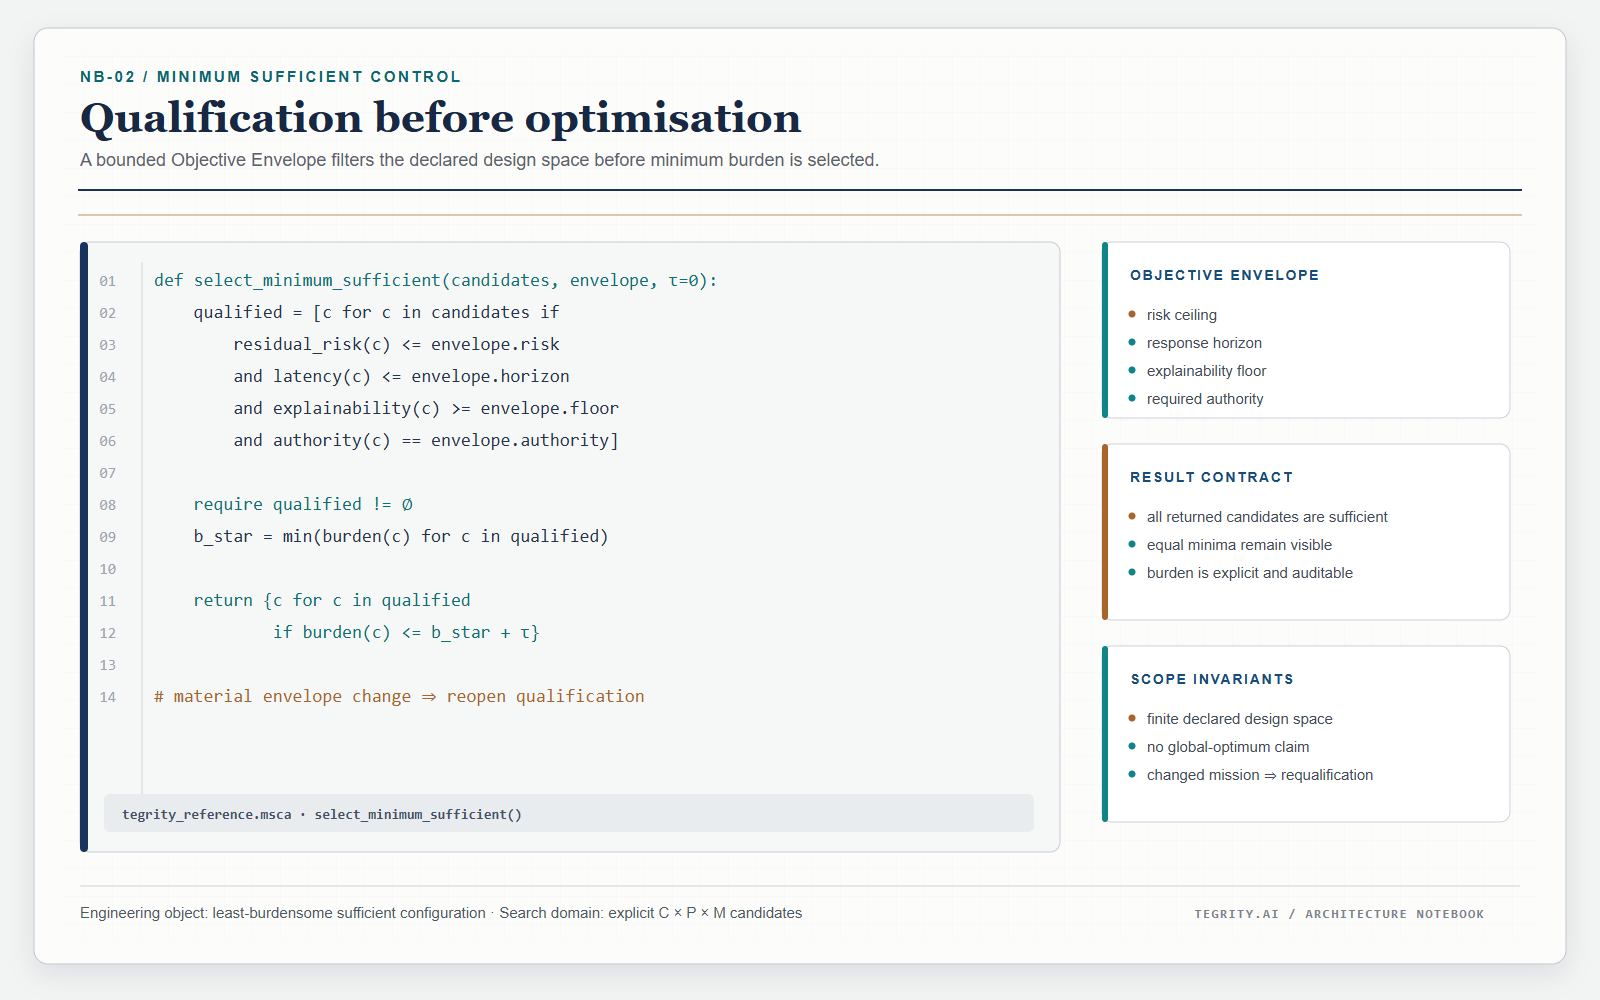
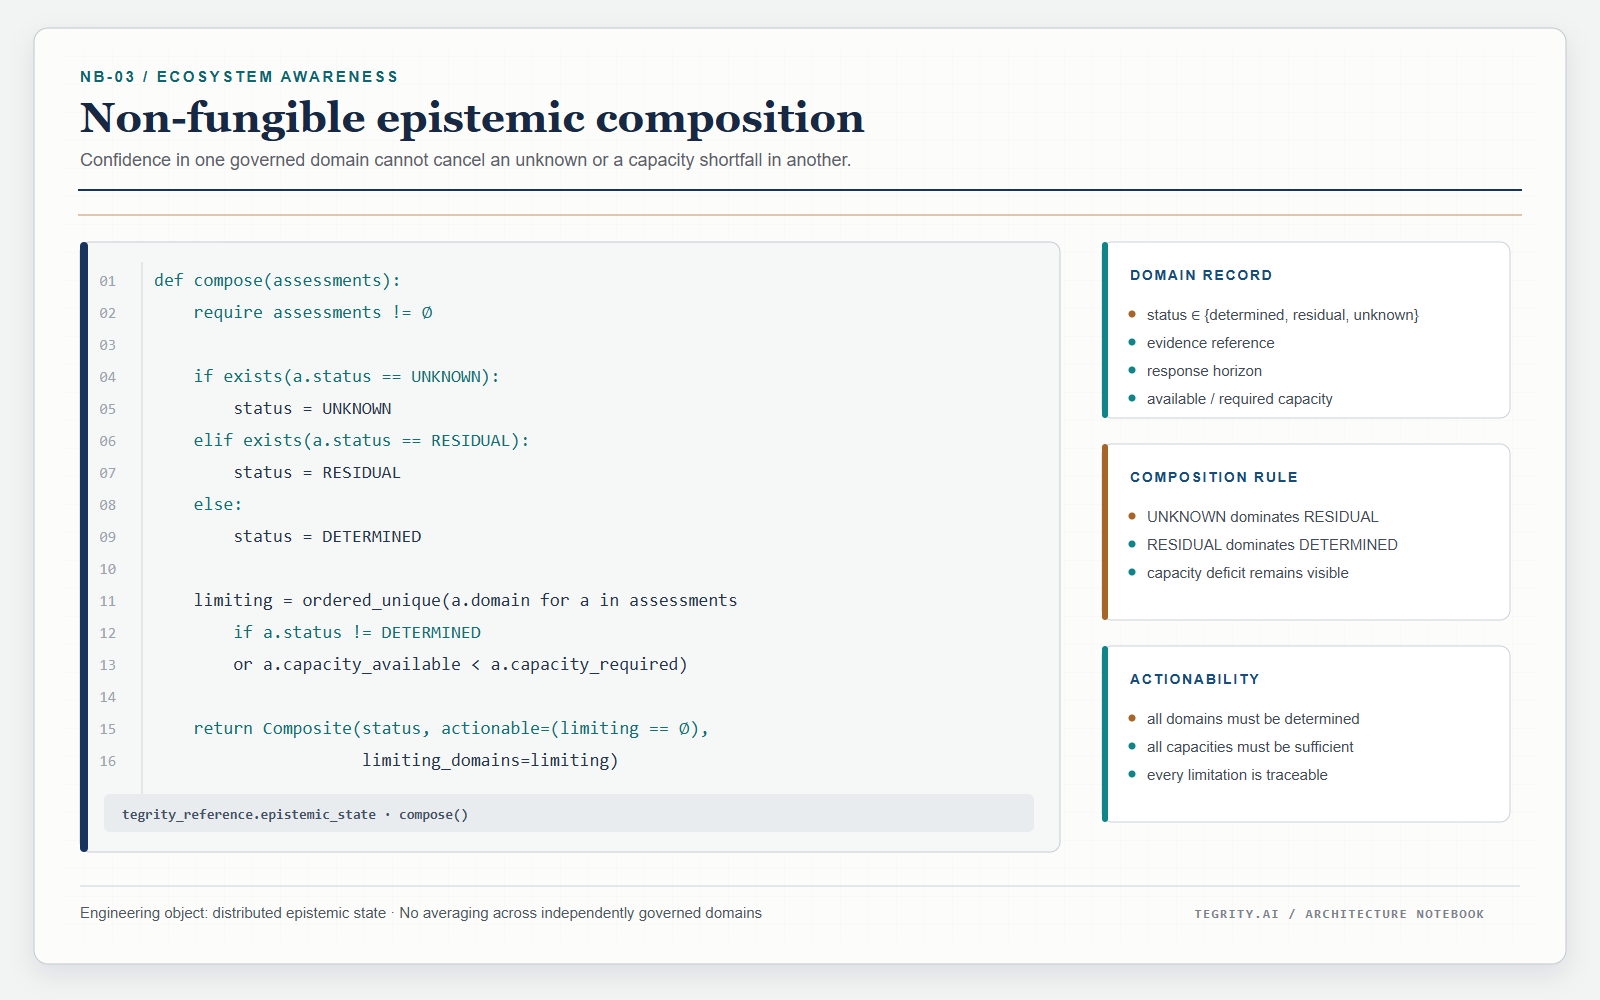
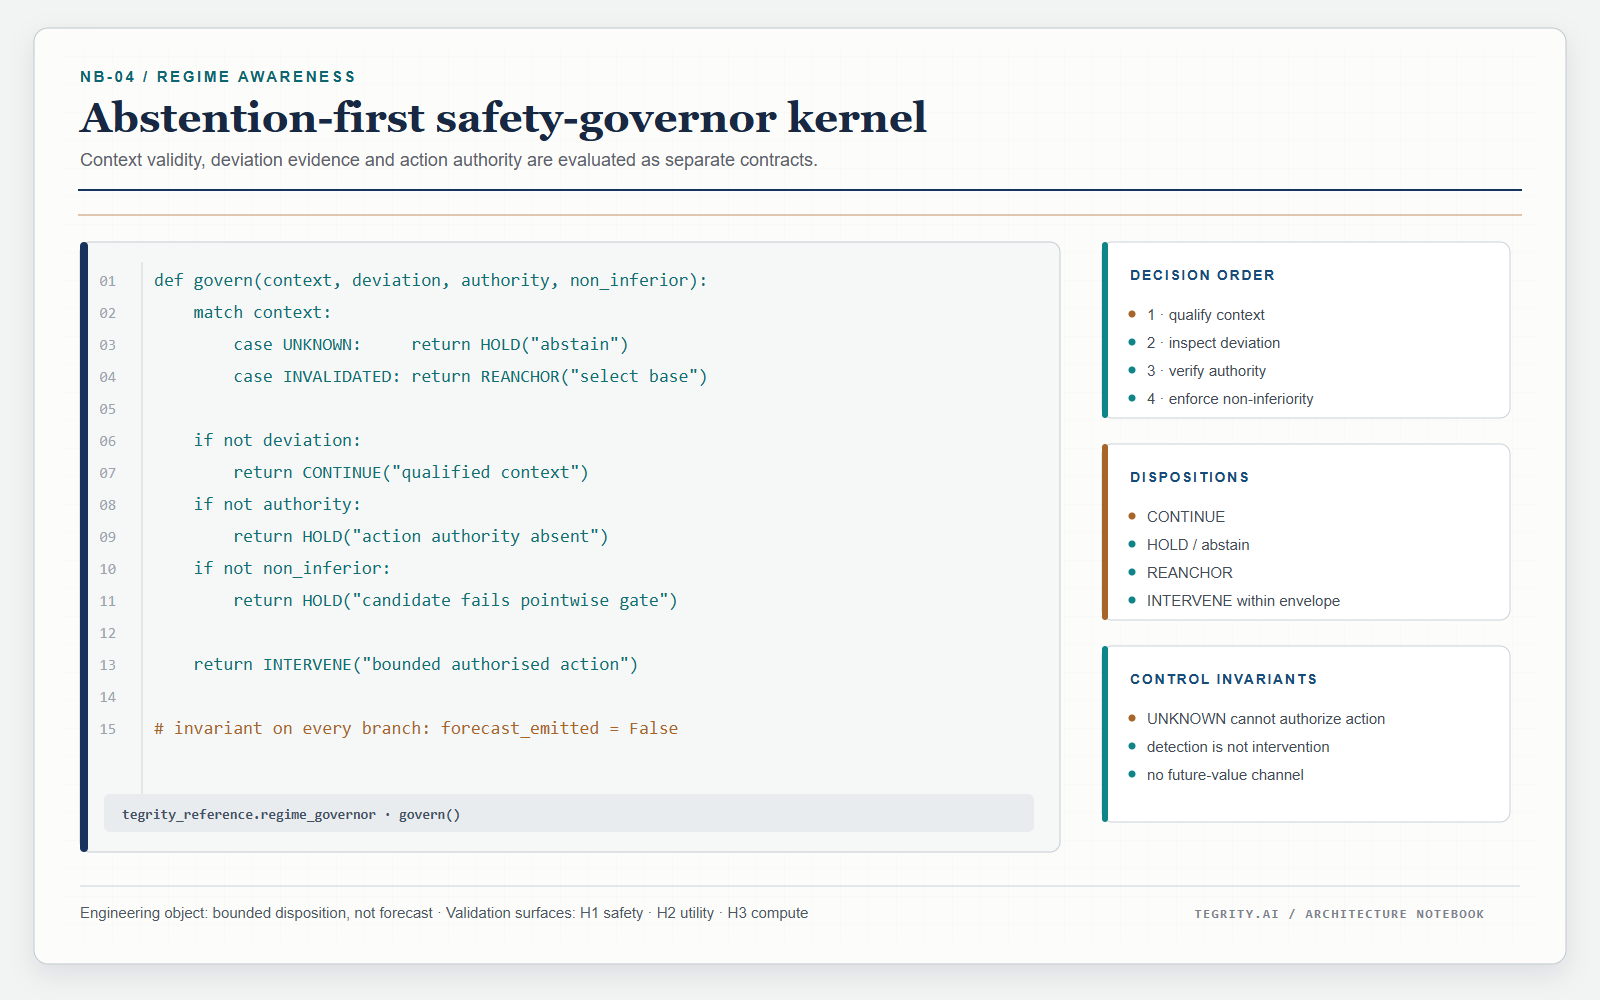
Four inspectable contract plates backed by dependency-free Python source, demos, nine tests and a SHA-256 manifest. Research prototype; not production safety logic.
Download Python reference (.zip)§ 04
Pre-standardization roadmap
A compact contribution path from research and field evidence into evaluation, architecture and standards-facing work.
Completed / established work
- Enterprise Estonia / EIS RUP proposal — submitted under reference 943697, with TalTech supporting the proposed research programme on minimum information, Cost of Clarity, transformation risk and structural-awareness foundations.
- Universitat de València — QAVA (GIUV2026-019) — research review across Regime Awareness, Early Warning, optimization and computational validation.
- UNECE WP.5 — From Historical Mobility Orchestration to Minimum Sufficient Control: bounded coordination, externalities, cascading commitments and scenario planning.
- UN CSTD — Working Group on Data Governance at All Levels — Information Outside the Readiness Sampling Frame: tacit/distributed knowledge, undeclared information, retrieval friction and readiness boundaries.
- IGF / IG Labs — AI for Learning / Tacit Knowledge: community learning, tacit-knowledge transmission and ethical integrity challenges in AI-supported learning.
Current pre-standardization work
- ITU-T FG-AI4SSC — Minimum Sufficient Control Architecture. FGAI4SSC-I-097 frames Minimum Sufficient Control as an architectural property around a declared Objective Envelope, coordination scope, operational mechanisms and enabling means.
- ITU-T FG-TIDA — Ecosystem Awareness. Current public work is centred on Theme #13, with interfaces to local verdict, human oversight and population/evidence layers, and with the determinacy / capacity handoff being developed as a candidate interoperable system-level building block.
Next contribution surface
- NIST AI TEVV / TEVV-Athlon — planned contribution on Ecosystem Awareness and Sufficiently Good Early Warning as evaluation surfaces for agentic AI: preserving residual indeterminacy, testing operating-frame validity and assessing whether warning is sufficient for the available response rather than assuming a perfect detector.
See the full list of research initiatives and their Field Notes in Research Initiatives, and the submitted contribution documents in Research Contributions.
§ 05
Industry Reference Group
The AI Integrity Management Industry Reference Group connects this roadmap with real architectures, products and operating cases. Participants can contribute requirements, implementation evidence, architecture mappings and reference cases while the candidate concepts and interfaces remain open.
AI Integrity Management — Industry Reference Group. Sponsors, patrons, contributors & members.
Learn more§ 06
Last Publications
| Series | Title | Date |
|---|---|---|
| Applied Research | From Field Practice to Pre-Standardization: An Extensible Case-Study Framework | 15 September 2026 |
| Applied Research | Minimum Sufficient Control Architecture for AI Enabled Urban Systems | 15 September 2026 |
| The Cost of Clarity | About Cats, Boxes and Enterprise Management Decisions | 8 July 2026 |
| — | Structural Awareness | 24 June 2026 |
Browse all publications and Field Notes. The full corpus index is maintained in Structural Awareness Program.